Series Context: We’ve stress-tested our infrastructure under extreme load (Day 171). Now we pivot from performance to security. If load testing asks “how much can this handle?”, penetration testing asks “how far in can an attacker get?” These two disciplines together give you a complete picture of your system’s resilience in production.
What We’re Building Today
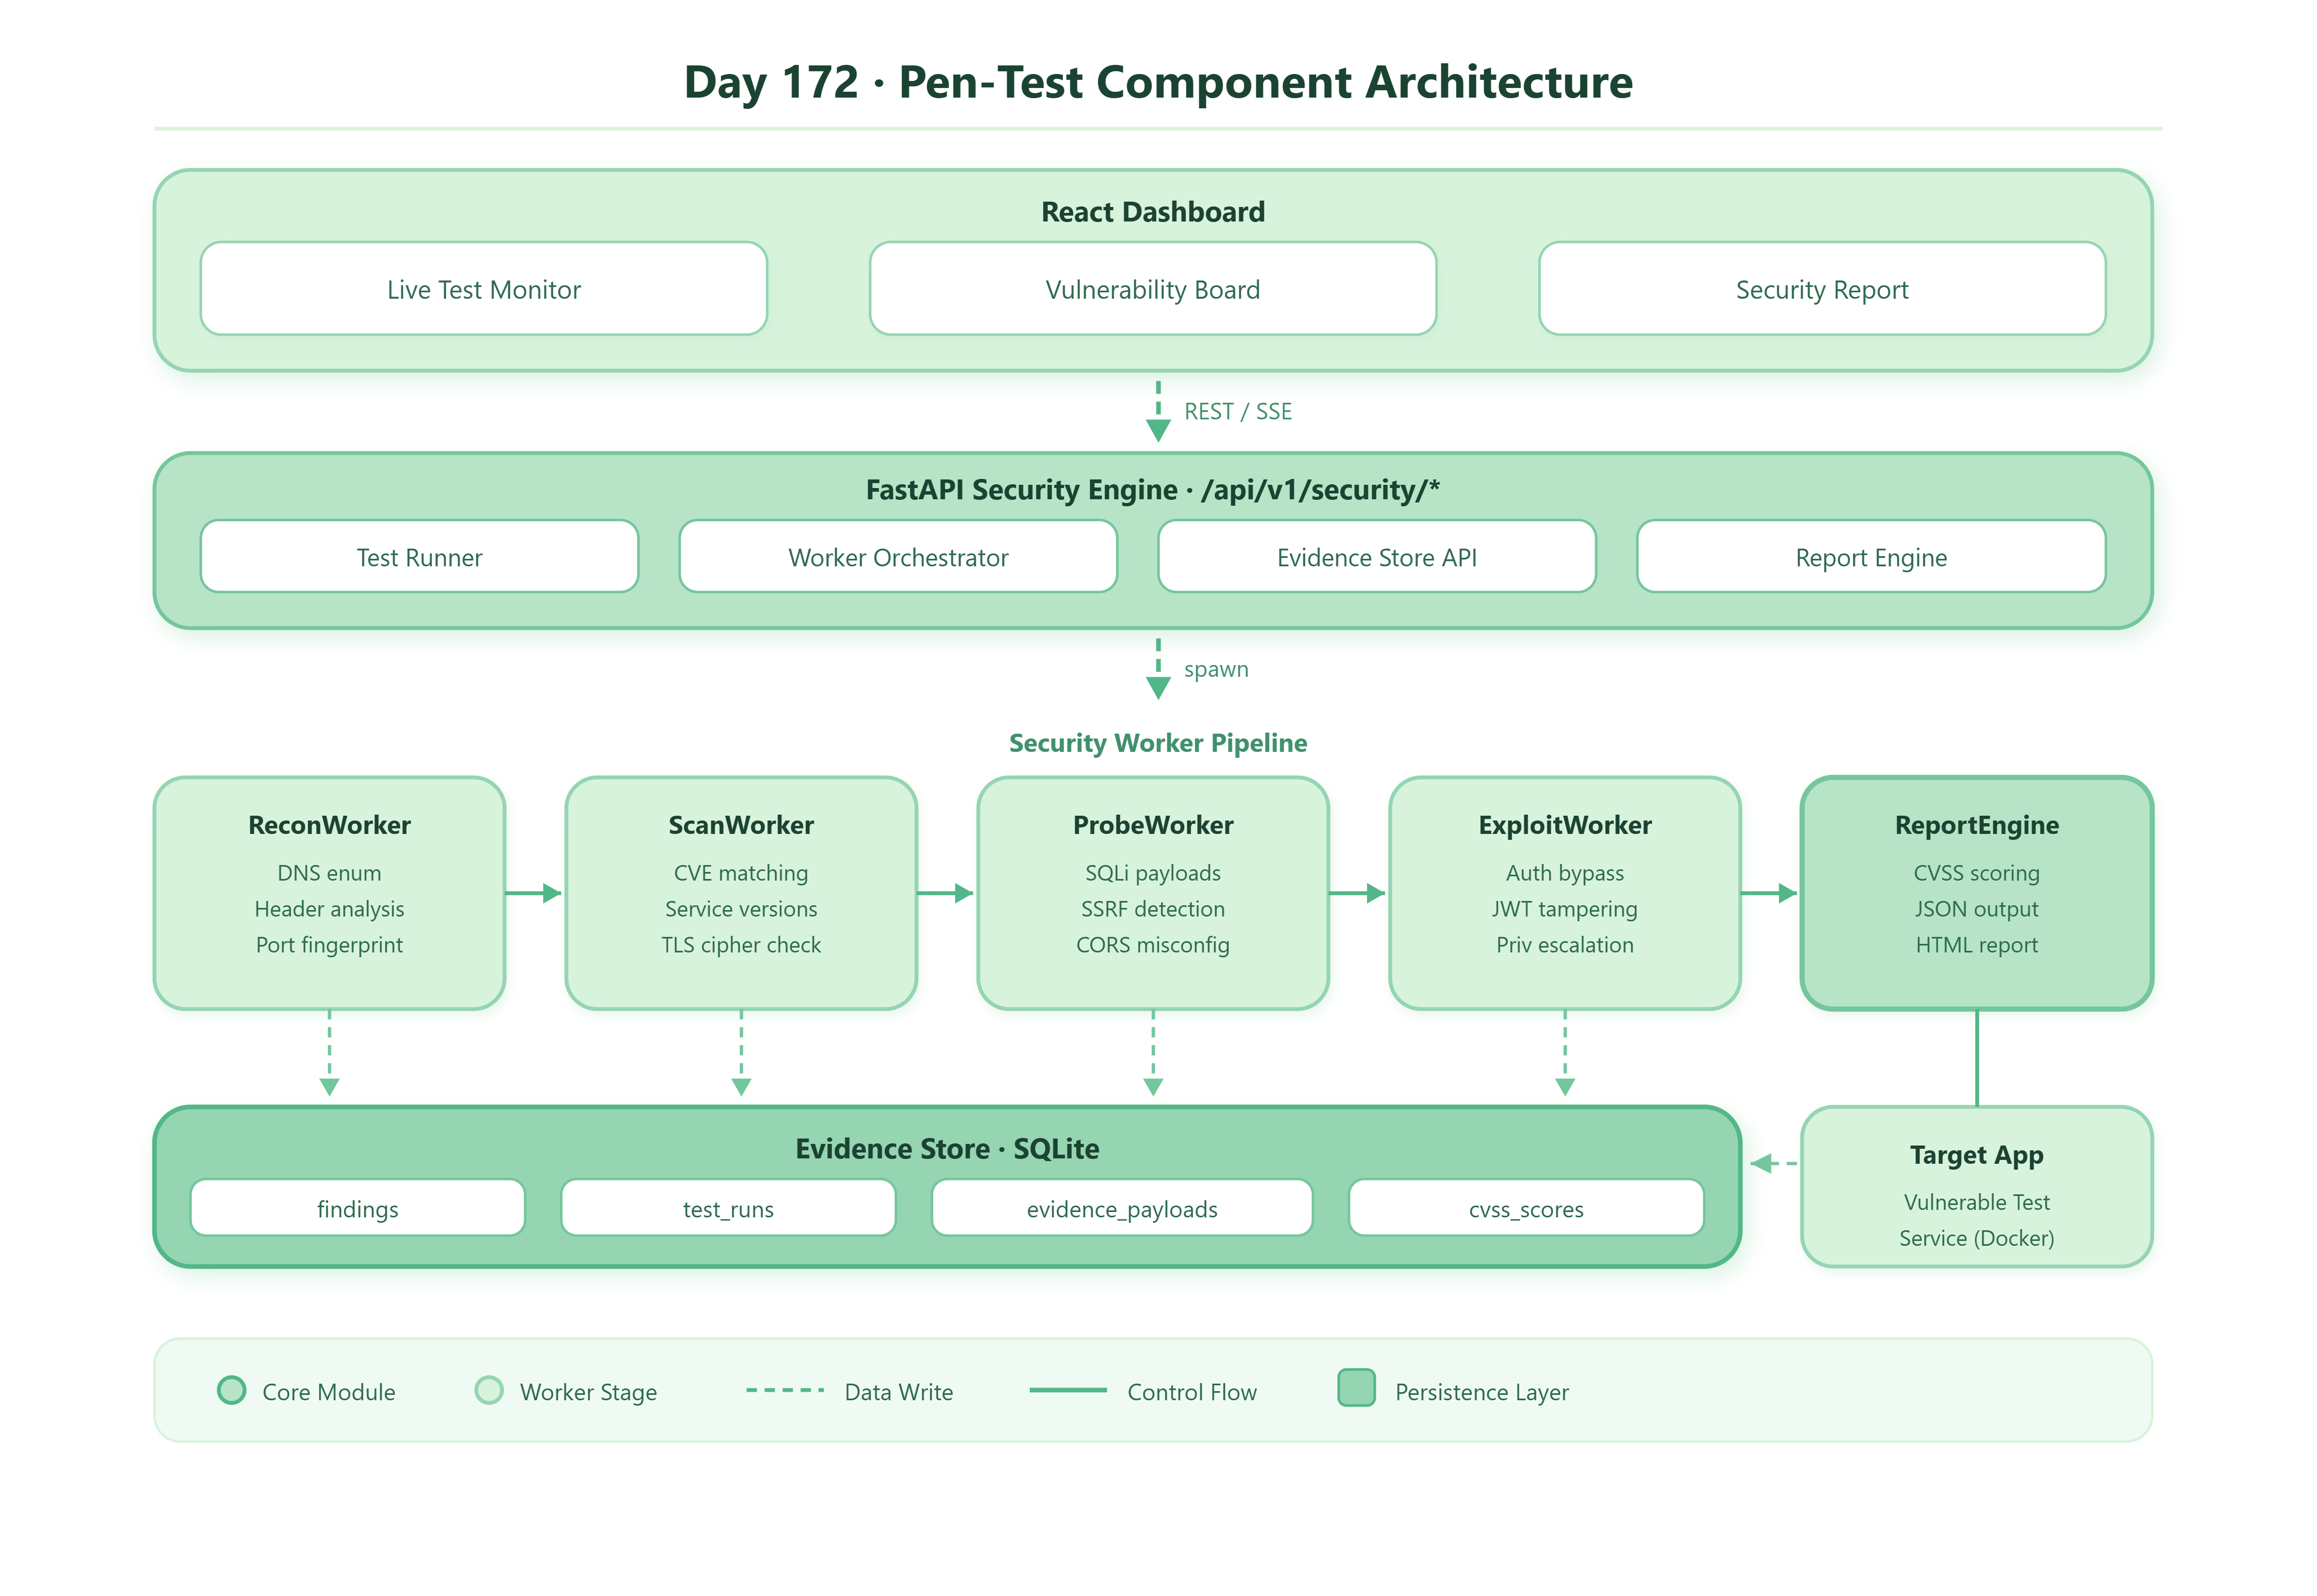
Automated pen-test orchestration layer — Python-based engine that chains reconnaissance → scanning → exploitation → reporting
Vulnerability Assessment Dashboard — React UI that mirrors tools like Burp Suite’s reporting console and Snyk’s vulnerability board
Security Control Validator — automated checks against OWASP Top 10 controls
Security Report Generator — machine-readable + human-readable output (JSON + PDF-style HTML)
The Architecture